Zagorath
Formerly /u/Zagorath on the alien site.
- 8 Posts
- 119 Comments
 1·6 months ago
Perhaps, but I’m describing something slightly different. Your description is basically “one platform supporting two protocols that basically do the same thing”. I’m talking more about “one app that has two separate-but-related bits of functionality, each using the more appropriate protocol for that job”.
Sounds like you need to upgrade your toaster, noob.
I mean, there’s nothing technically stopping one app supporting both protocols natively, especially since Lemmy already includes a field for people’s profiles to link their Matrix ID. Though to my knowledge none do it yet.
Personally I think if LW wants to ban a certain kind of content, more power to them. But they should be transparent about it.
If they’ve said they’ll unban pirate content, then pirate content should be allowed. If they want it banned, fine, but make a statement clarifying that that is the case.
OP is doing good work by pointing this out.
 3·7 months ago
Your 142.x.x.x will be your public IP address. All devices on your network share that public IP. They all have a unique private IP address too, accessible only on your network. It probably starts with 192.168.x.x, but it could be 10.x.x.x or even less likely 172.16–31.x.x.
If you want to operate a web server that users can go to by typing https://youdomain.com/, you’ll need to forward from ports 80 and 443 through to the internal IP address of your server, using the “port forwarding” settings on your router. What port on the internal IP you route to depends on how your server is configured. But a basic default configuration is fairly likely to be 80 and 443, too.
Since you have a reverse proxy, all traffic from your router should go to that. Then you use that to send the appropriate traffic to the appropriate server based on whatever rules you want to apply. (e.g. siteone.mydomain.com goes to server 1, sitetwo.mydomain.com goes to server 2, or mydomain.com/siteone goes to server 1, etc.).
Oh good tip!
That’s a pretty righteous set up OP.
Lol not me. I’m not the author. Just saw the article and thought it was an interesting conversation starter.
or a recipe for an insecure mess that could become difficult to maintain
The concept, or the specific setup the author of that article has? If you mean the latter, I’m not going to argue. But the concept? It shouldn’t have any effect either way on security, but the whole advantage of it is that it’s less of a mess. The same way that running a whole bunch of services on bare metal can quickly become a mess compared to VMs or Docker/LX containers, declared state helps give a single source of truth for what all the services you might be running are. It lets you make changes in repeatable and clearly documented ways, so you can never be left wondering “how did I do that before?” if you need to do it again.
If everything you run is a Docker container, there’s a good chance Terraform is overkill; a Kubernetes config will probably do the job. But depending on your setup there are a whole bunch of different tools that might be useful.
What’s your preferred approach to defined state in your home servers?
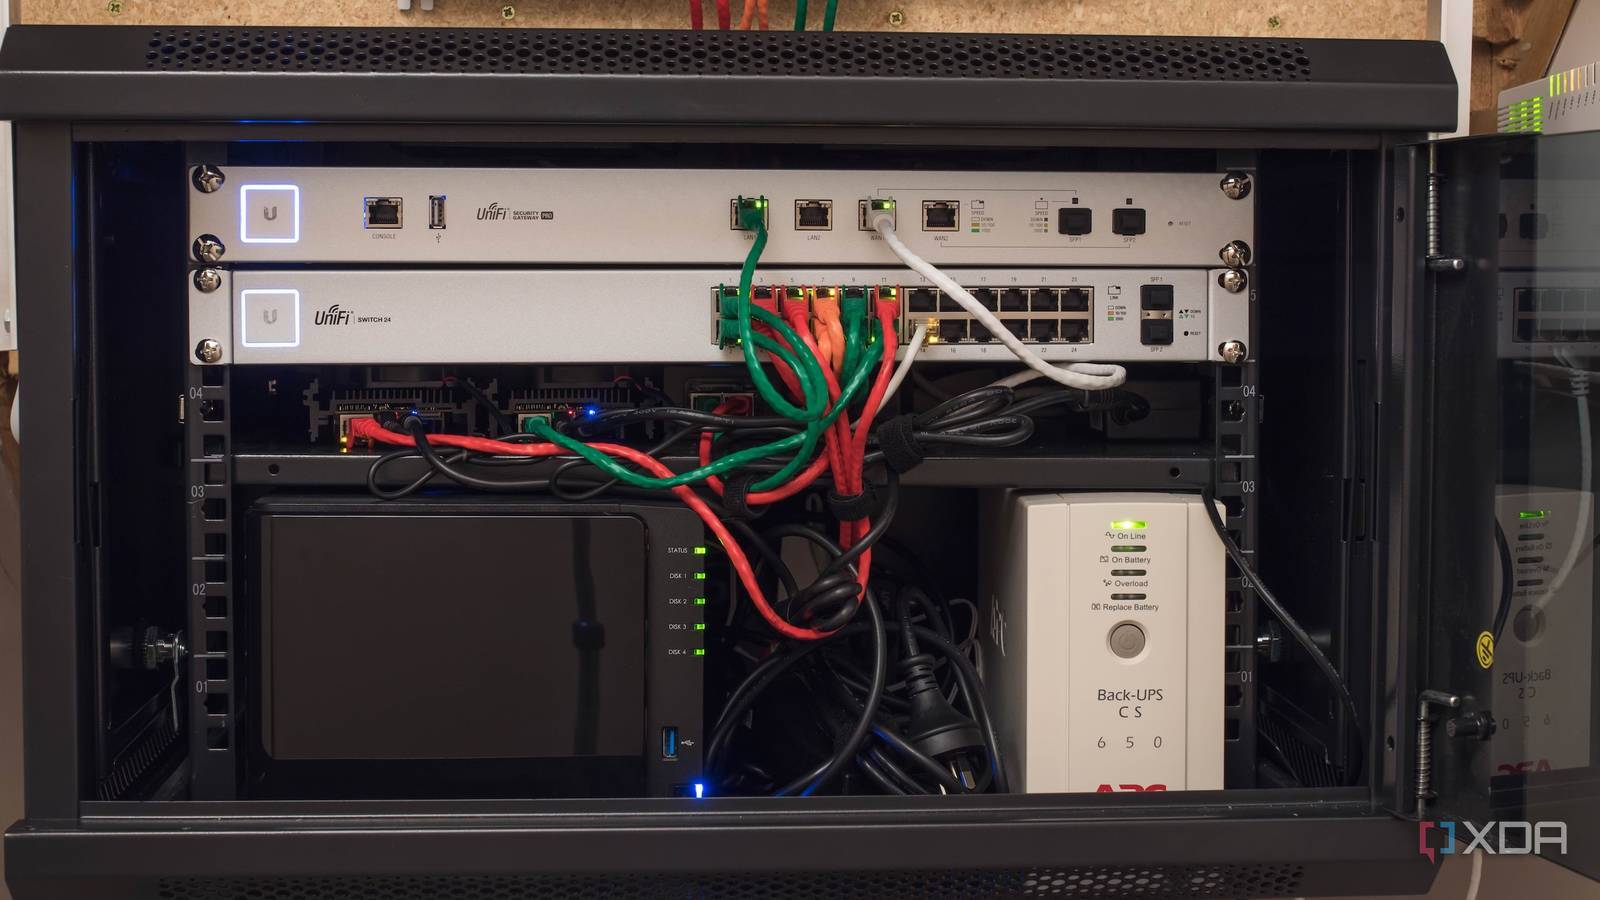
Oh, I used HA to mean high availability. I was not aware people also abbreviated Home Assistant.
Sorry for the late reply. I’m just disorganised and have way too many unread notifications.
LXC containers sound really interesting, especially on a machine that’s hosting a lot of services. But how available are they? One advantage of Docker is its ubiquity, with a lot of useful tools already built as Docker images. Does LXC have a similarly broad supply of images? Or else is it easy to create one yourself?
Re VM vs LXC, have I got this right? You generally use VMs only for things that are intermittently spun up, rather than services you keep running all the time, with a couple of exceptions like HomeAssistant? What’s the reason they’re an exception?
Possibly related: your examples are all that VMs get access to the discrete GPU, containers use the integrated GPU. Is there a particular reason for that distribution?
I’m really curious about the cluster thing too. How simple is that? Is it something where you could start out just using an old spare laptop, then later add a dedicated server and have it transparently expand the power of your server? Or is the advantage just around HA? Or something else?
Sorry for the late reply. I’m just disorganised and have way too many unread notifications.
LXC containers sound really interesting, especially on a machine that’s hosting a lot of services. But how available are they? One advantage of Docker is its ubiquity, with a lot of useful tools already built as Docker images. Does LXC have a similarly broad supply of images? Or another easy way to run things?
Oh yeah, the “run headless” tip too was great! I would never have used a desktop environment, and would in effect have been using it headless. But had you and others not specifically suggested running it as headless it would probably not have occurred to me that that’s a setting change I’d need to make while installing it.
Thanks! I genuinely wasn’t sure how much RAM would be necessary, and would have probably seriously considered 8 GB enough if I hadn’t gotten the feedback.
I’ve no comments on RISC-V, but I agree that a move towards ARM in the Windows & Linux worlds would seem sensible. I would guess it hasn’t happened for the same reason IPv6 hasn’t taken over. Too much momentum. Too many developers still working in an x86 world, too many legacy apps that won’t easily run on ARM, too many hardware manufacturers each making the individual choice to keep making the current-popular option. Apple could transition because they’re the single gatekeeper. They make the decision, and everybody else who wants to use a Mac has to follow along. I’m going to guess that the control they have over the hardware and the software also means Rosetta 2 works a hell of a lot better than Microsoft’s Prism. (I can’t say for sure, having never used an ARM-based Windows machine or an ARM-based Mac.)
In terms of heat, what kind of room do you have it in? Somewhere with good natural airflow, or away in a closet somewhere?
I guess I have the same question for you as I did for curbstickle. What’s the advantage of doing things that way with VMs, vs running Docker containers? How does it end up working?
Interesting. I’ve never really played around with that style of VM-based server architecture before. I’ve always either used Docker (& Kubernetes) or ran things on bare metal.
If you’re willing to talk a bit more about how it works, advantages of it, etc., I’d love to hear. But I sincerely don’t want to put any pressure and won’t be at all offended if you don’t have the time or effort.

Worth noting that Lemmy receives at least some institutional funding for its development. And I believe some of that funding is contingent on hitting active user goals or similar metrics.